
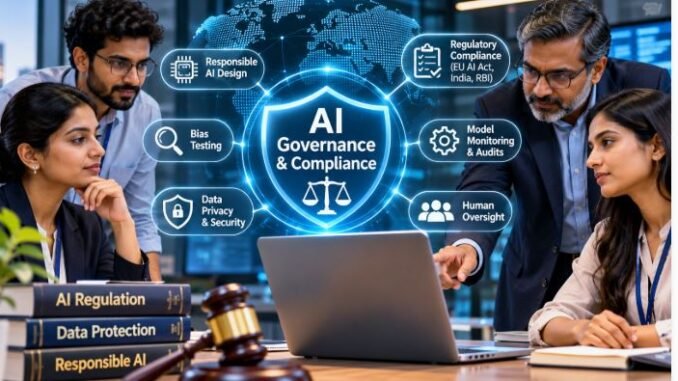
Artificial intelligence is changing how businesses operate, from customer service and financial decisions to product development and data analysis. As companies adopt AI tools at a faster pace, questions around safety, transparency, privacy and accountability are becoming increasingly important.
For technology companies, developing an AI system is no longer just about making it faster or more efficient. Businesses must also understand how it makes decisions, what data it uses and whether its outcomes are fair and reliable. Regulators across different markets are paying closer attention to these issues, making AI governance and business compliance important parts of modern business strategy.
This shift is changing how technology companies design products, manage risks and prepare for long-term growth.
AI Governance Is Becoming a Business Priority
In the early stages of AI adoption, many companies focused mainly on innovation and operational efficiency. Governance often received attention only when a problem emerged. That approach is becoming harder to maintain as AI systems influence decisions that can directly affect customers, employees and businesses.
For example, AI tools may help banks assess loan applications, companies screen job candidates or businesses determine customer pricing. If these systems produce biased or inaccurate results, the consequences can extend beyond technical errors and create legal, financial and reputational risks.
As a result, companies are increasingly expected to establish clear rules for how AI systems are developed, tested, deployed and monitored. Responsible AI is moving from a technology concern to a wider management and business responsibility.
New AI Regulations Are Changing Business Expectations
Governments and regulatory authorities are developing frameworks to address the risks associated with artificial intelligence. These rules differ across countries, but many share a common objective: ensuring that AI systems are used safely, transparently and responsibly.
The European Union’s AI Act is an important example. It introduces a risk-based approach, placing stricter requirements on certain high-risk AI applications. Businesses operating in or serving the European market need to understand which obligations apply to their systems.
In India, the growing focus on AI governance is also encouraging companies to pay greater attention to responsible innovation, data protection and accountability. Regulatory and policy discussions, including the RBI’s FREE-AI framework for the financial sector, reflect the increasing importance of managing AI-related risks.
For technology companies operating internationally, the challenge is more complicated. They may need to meet different regulatory expectations depending on where their products are developed, deployed and used.
Transparency and Accountability Are Becoming Essential
One of the biggest concerns surrounding AI is the difficulty of understanding how some systems reach their decisions. A company may use an automated model to approve a financial application or recommend a particular service, but customers may not always know why that decision was made.
This is creating greater demand for explainable AI and clear accountability.
Businesses need to understand the information used by their systems, test whether outcomes are fair and maintain records that help explain important decisions. When an AI tool affects people’s finances, employment or access to services, human oversight becomes particularly important.
For technology companies, transparency is not simply about meeting regulatory expectations. It can also help build customer confidence and strengthen relationships with business partners.
AI Risk Management Must Cover the Entire Technology Lifecycle
AI governance does not end when a product is launched. Risks can emerge during development, testing, deployment and everyday use.
A model that performs well during initial testing may produce different results when exposed to new data or changing customer behaviour. Security weaknesses, inaccurate information and biased outputs can also affect performance over time.
Technology companies are therefore moving towards continuous monitoring rather than relying only on occasional reviews. This includes testing models, checking data quality, reviewing system performance and maintaining audit records.
Third-party technology providers also require attention. Businesses that use external AI models or software services need to understand how those systems handle information and what risks they may introduce.
The growing use of unauthorised AI tools within organisations, often described as shadow AI, adds another layer of concern. Clear internal policies and employee awareness can help businesses manage this risk.
Compliance Is Becoming a Shared Responsibility
AI governance cannot be handled by technology teams alone. Legal departments, cybersecurity specialists, product managers, data teams and compliance professionals all have a role to play.
Engineers may be responsible for testing model performance, while legal teams assess regulatory obligations. Security professionals examine vulnerabilities, and product managers ensure that safeguards are considered during product development.
Senior management and boards also need visibility into how AI is being used across the organisation. Clear responsibilities make it easier to identify problems, respond to incidents and maintain consistent standards.
This cross-functional approach can help companies avoid treating compliance as a last-minute approval process. Instead, governance becomes part of everyday business operations.
Building Compliance Into AI Products From the Beginning
Technology companies are increasingly recognising the value of considering governance before an AI product reaches customers. Adding safeguards after deployment can be expensive and may require major changes to a product.
A more effective approach is to include risk assessments, privacy controls, bias testing and human review during the design and development stages.
Companies can also establish internal approval processes for new AI applications. These processes help determine whether a system is suitable for its intended purpose and whether additional safeguards are required.
Building compliance into product design can reduce the risk of costly changes later. It can also make it easier for businesses to demonstrate that they have taken responsible steps before introducing AI-powered services to the market.
The Business Impact: Higher Costs but Stronger Long-Term Trust
Meeting new AI governance expectations requires investment. Companies may need additional compliance professionals, testing systems, monitoring tools and employee training. Smaller technology businesses and startups may find these requirements particularly challenging because of limited resources.
However, responsible AI practices can also create business advantages.
Companies with clear governance systems may find it easier to work with enterprise customers, financial institutions and partners that expect strong risk controls. Transparent AI products can also improve customer confidence and reduce the likelihood of reputational damage caused by poorly managed systems.
For investors and business leaders, AI governance is becoming an important consideration when evaluating the long-term strength of technology companies.
The real business challenge is finding the right balance between innovation and responsibility. Companies need to continue developing useful AI products while ensuring that the risks are properly understood and managed.
Conclusion
AI governance and business compliance are becoming central to the future of the technology industry. As artificial intelligence takes on a larger role in business decisions, companies are facing greater expectations around transparency, accountability, security and responsible use.
For technology businesses, adapting to this changing environment will require more than understanding new regulations. It will involve building governance into product development, strengthening internal controls and ensuring that different teams share responsibility for AI-related risks.
Companies that take these steps can do more than prepare for regulatory scrutiny. They can build stronger customer trust, improve business resilience and create a more reliable foundation for future AI innovation.
